Is Your Mobile App Ready for AI-Amplified Fraud? Find Out With a Free Security Audit
AI is making cyberattacks faster, more automated, and easier to scale. Attackers can now use AI to accelerate vulnerability discovery, automate reconnaissance, generate convincing phishing and social-engineering attacks, create malicious code, and adapt attack techniques faster than traditional defenses can respond.
As AI continues to evolve, mobile security also needs to evolve with it. Security controls that were designed to defend against yesterday's attacks may not be enough against faster, more adaptive, and increasingly automated threats.
But here's the critical question:
Is your mobile app actually ready to withstand these modern attack techniques?
Bugsmirror's free mobile app security audit helps you find out. The audit evaluates your application on a real physical device under simulated attack conditions, helping identify runtime threats, security weaknesses, device integrity risks, and controls that attackers may be able to bypass.
Don't wait for attackers to discover your weaknesses. Find out how ready your app is today.
Is your mobile app ready for modern fraud?
This is a real audit, not a demo. It is an automated runtime security audit performed on a real physical device. You receive a professional security report that evaluates how strong your app’s security controls are under real-world attack conditions, including runtime threats, device integrity risks, and security bypass attempts.
The runtime security audit focuses on mobile DAST, the most ignored yet most exploited attack surface today. We test your app against device integrity, app tampering, OS integrity, secure communication, mobile privacy, mobile fraud, and even social engineering.
The assessment can also help identify security gaps relevant to applicable industry standards and regulatory expectations, including:
- OWASP MASVS
- RBI security requirements
- SEBI Cybersecurity and Cyber Resilience Framework (CSCRF)
- NPCI security requirements
- GDPR
For applications handling payments, authentication, sensitive APIs, or user data, identifying these weaknesses early can help reduce security, fraud, compliance, and reputational risks.
The objective is simple: understand whether your security controls work when they are actually challenged.
What happens when attackers put your app to the test?
Your application may already have encryption, authentication, SSL pinning, anti-tampering, root or jailbreak detection, and other security controls.
But the real question is:
Can those controls withstand an attack?
The audit simulates attacker behavior to assess whether security controls are properly implemented and whether they can be circumvented.
The assessment can identify situations where:
- A required security control is missing.
- A security control is implemented but ineffective.
- An attacker can manipulate application behavior at runtime.
- Application or device integrity can be compromised.
- Existing protections can be bypassed.
- Security mechanisms do not behave as expected under attack conditions.
This gives your security and development teams a more practical view of application risk.
Already using RASP? Find out if it can actually stop an attack
Having a RASP solution integrated into your mobile application does not automatically mean every runtime threat is blocked.
The important question is whether your existing runtime protection can withstand real bypass attempts.
Bugsmirror's security audit can also assess applications that already have RASP protection.
This helps you understand:
- Whether runtime security controls are working effectively.
- Which controls successfully detect or prevent attacks.
- Whether specific protections can be bypassed.
- Where your current RASP implementation may need improvement.
- Whether your application's runtime security posture matches your expectations.
Don't just assume your RASP works. Test it.
Why sharing your app link for a free security audit is safe and smart?
The audit is safe, confidential, and largely automated. Your app is tested in an isolated environment on a real physical device. We simulate real attacker behaviour by attempting bypass, security parameter manipulation, and runtime abuse. This gives you a true picture of how protected your app is against real-world attack conditions.
The process is simple:
- Just log in with your business email.
- Provide playstore/appstore link, or .apk/.ipa file of your application.
- We will send you a free audit report to your email in 24 hours.
Know exactly where your app's security stands
You receive a structured security report that gives you a clear view of your application's security posture.
The report includes:
- Threat severity: High, Medium, or Low
- CVSS risk scores: Risk ratings based on the Common Vulnerability Scoring System
- OWASP-aligned categories: Classification of identified security issues
- Pass / Fail / Bypassed results: Clear status of individual security controls
- Exploitability context: Additional information to help understand the practical risk
What do pass, fail, and bypass mean?
- Pass means the security control is properly implemented and successfully withstands the tested threat.
- Fail means the expected security control is not present or does not meet the required security check.
- Bypassed means the security control exists, but the audit was able to circumvent it during testing.
This distinction is important because an application can have a security control in place and still remain vulnerable if that control can be bypassed.
The report helps developers prioritize remediation, gives security teams visibility into application risk, and helps leadership understand where security improvements are needed.
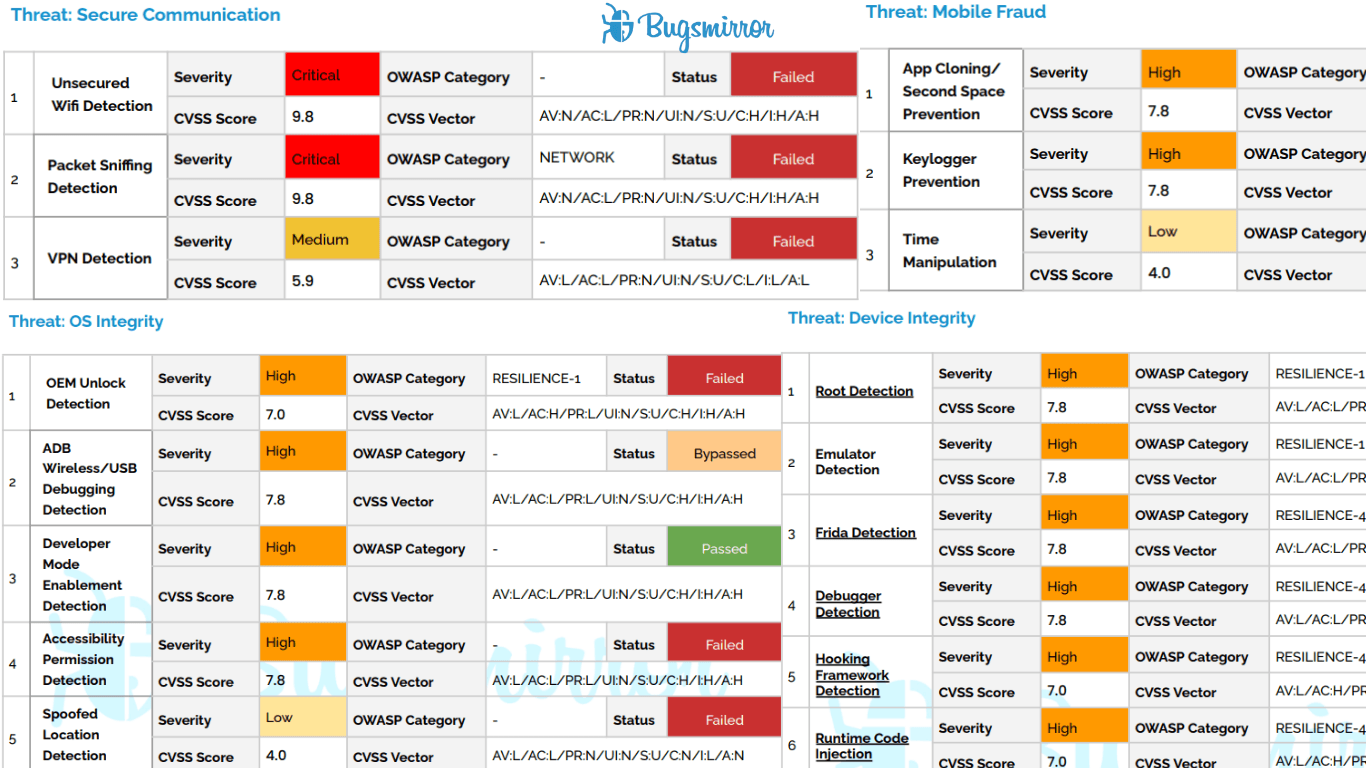
Get a sample report for more information.
Who should take the free mobile app security audit?
The audit is relevant to organizations whose mobile applications handle sensitive information, authentication, payments, APIs, or business-critical operations.
It can be particularly useful for:
- Fintech and banking applications
- UPI and payment applications
- E-commerce applications
- Healthcare applications
- Edtech applications
- Applications handling sensitive APIs
- Applications processing payments
- Applications handling personal or financial data
- Startups preparing for funding or enterprise onboarding
- Organizations launching a new mobile application or major release
You should also consider taking the audit if you are:
- Looking for a free mobile app security assessment.
- Preparing for applicable security or regulatory requirements.
- Facing mobile application security concerns.
- Preparing for enterprise customer onboarding.
- Launching a new application version.
- Evaluating your current mobile security posture.
- Using RASP and want to validate whether it can be bypassed.
Why Bugsmirror?
Bugsmirror specializes in mobile application security and helps organizations identify, test, and protect against mobile security threats. Bugsmirror has reported and been acknowledged for 1,250+ Android bugs/vulnerabilities, demonstrating extensive experience in identifying mobile application security weaknesses.
Its mobile application security platform, Bugsmirror MASST, brings together capabilities for security testing, runtime protection, and threat visibility. The platform includes capabilities across application security testing and runtime protection, helping organizations address mobile security across different stages of the application lifecycle.
Why wait? Get your free security audit report now!
Share this article
Help others discover this content
Don’t give fraud a way in. Secure every layer of your mobile app.
100M+
Users Protected
100+
Apps Secured
1000+
Apps Hardened